In short
SentinelOne Singularity is a security platform that protects endpoints, servers and cloud workloads from one agent and console. The agent prevents, detects and responds autonomously, including rolling devices back after ransomware on supported systems. Singularity Complete adds EDR and XDR, with identity, Purple AI and managed services as options. Forever Systems can quote and set it up.
Get a quote for SentinelOne Singularity
Tell us roughly how many users or sites you have and we will come back to you with options and a quote.
How the Singularity agent works
The Singularity agent runs AI models on the device to block known and unknown malware before it executes, and watches behaviour to catch fileless attacks, script abuse and exploits. When it detects malicious activity it can respond by itself: kill processes, quarantine files, disconnect the device from the network while keeping it connected to the console and, on supported systems, roll the device back to its state before the attack.
Because detection and response happen on the device, protection continues when a laptop is offline, and events sync to the console when it reconnects. The console, data lake and investigation tools run in SentinelOne's cloud. Agents cover Windows, macOS and Linux, including virtual desktops, and the same platform extends to cloud workloads.
EDR and XDR depth
SentinelOne's EDR starts at Singularity Complete, with 14 days of searchable data; Singularity Commercial adds identity threat detection and response, managed threat hunting and 90 days of data. For the package-by-package comparison, see SentinelOne antivirus (opens in a new tab) and SentinelOne Singularity Control (opens in a new tab) on our sister site.
In Complete, correlated Storylines link related events on a device into one chain, so an analyst sees the whole attack rather than a stream of single alerts, and Deep Visibility search lets your team or a provider hunt across the stored telemetry. Package contents are revised from time to time, so we confirm what is included at quote.
Ransomware rollback
Rollback is one of the features buyers ask about most. When the agent detects ransomware on a supported system it can reverse the changes the attack made, restoring encrypted files and settings, rather than leaving you to rebuild the device. That can turn a ransomware alert into an afternoon's clean-up instead of a restore project.
Treat it as a recovery aid, not a backup. Keep independent, immutable backups as well, and test restores; our guide on how to prevent ransomware attacks covers the full picture.
Is SentinelOne Singularity the right fit for you?
We will check it against your systems and requirements and recommend the right option.
Purple AI, identity, cloud and SIEM
Around the endpoint, SentinelOne offers:
- Purple AI: SentinelOne's AI security analyst, which answers investigators' questions in plain English without hand-written queries, summarises activity and helps triage alerts. SentinelOne's package page lists an AI Security Assistant from Complete and an agentic AI SOC analyst in Enterprise; ask us how it is licensed for your package.
- Singularity Identity: identity posture checks and identity threat detection and response for Active Directory and Entra ID, included from Commercial; see identity threat detection and response (opens in a new tab).
- Singularity Cloud: runtime protection for servers, virtual machines and containers; see cloud workload protection (opens in a new tab).
- AI SIEM and automation: ingest first and third-party logs and automate response workflows, if you want more than endpoint telemetry in one place. Our extended detection and response guide explains when that is worth it.
Managed detection and response
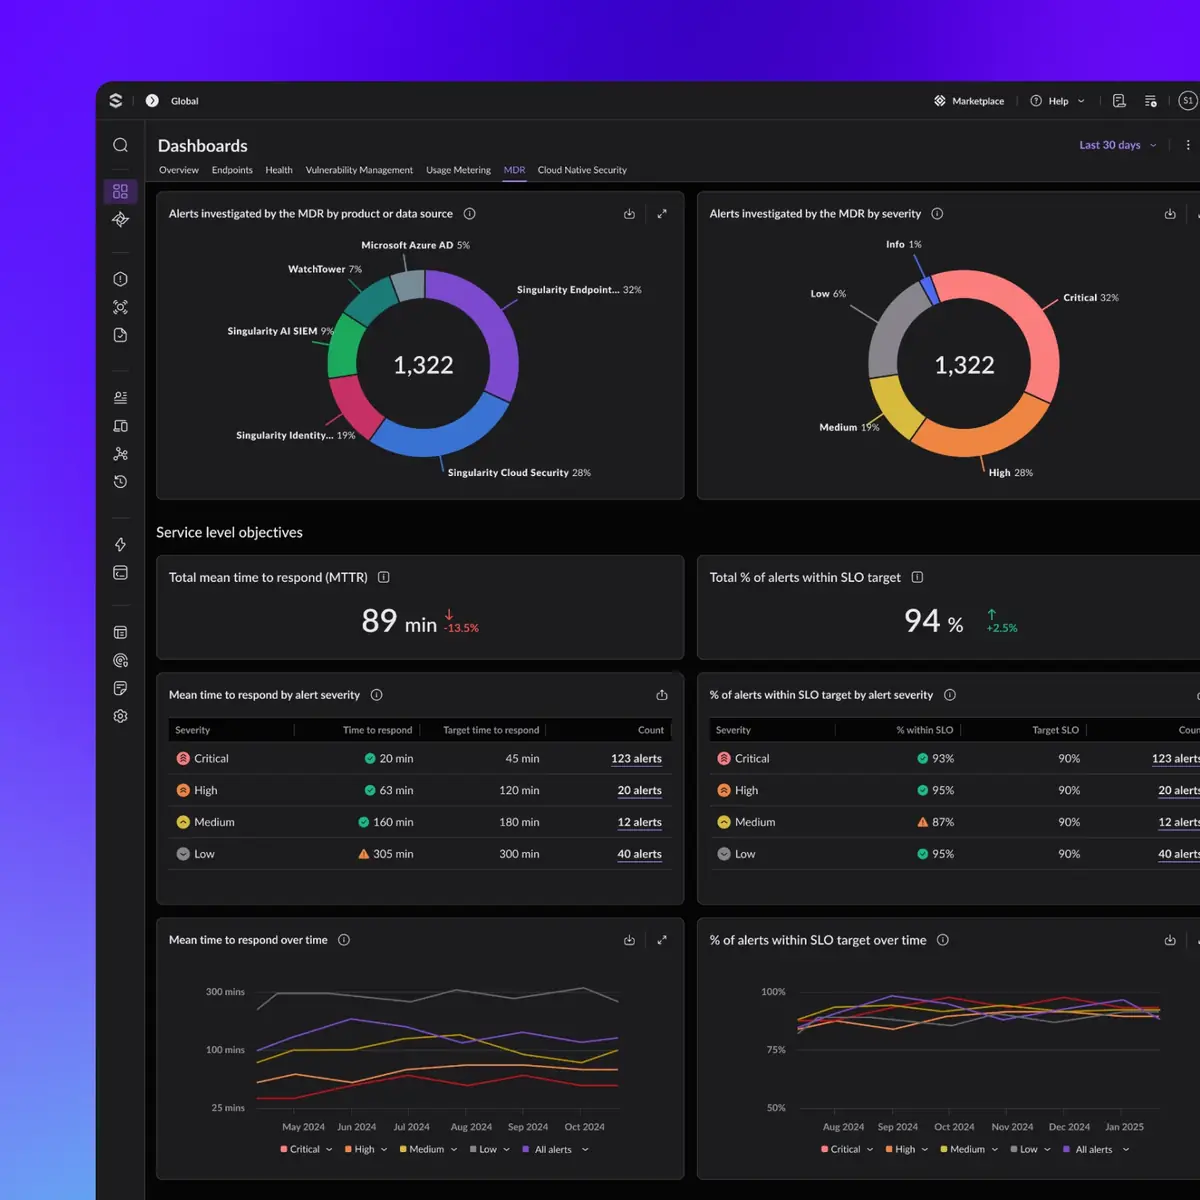
SentinelOne's own managed services sit under the Wayfinder name. Wayfinder MDR, formerly Vigilance MDR, puts SentinelOne's analysts on your console around the clock to investigate and respond within a policy you agree, and SentinelOne lists it as an add-on to its Commercial and Enterprise packages. Our guide to SentinelOne Vigilance MDR explains how it works.
Many IT providers also run their own MDR on the Singularity platform, so you can choose the vendor's service or a provider's. Whichever you choose, agree in writing which actions the service may take without asking and how out-of-hours escalation works. Our MSSP site compares managed detection and response (opens in a new tab) options.
Who SentinelOne Singularity suits
Singularity suits organisations that want strong automation on the device, mixed Windows, macOS and Linux estates, and teams that like the option of rolling back a ransomware-hit device rather than rebuilding it. Its identity and cloud options make it a single-vendor route for growing estates.
It is most often compared with CrowdStrike Falcon Insight XDR and Microsoft Defender for Endpoint; our CrowdStrike vs SentinelOne vs Defender comparison sets out the differences. If you only need antivirus-level prevention, see SentinelOne antivirus (opens in a new tab) on our sister site.
How we help
Forever Systems can quote and set up SentinelOne Singularity for you. A typical rollout starts with the agent in detect-only mode on a pilot group, so you can see what it would block and add exclusions for line-of-business software before switching to protect mode. Next come device and firewall control policies, then the wider estate in waves, with the previous product removed only once each device reports healthy. Servers and virtual desktops usually get their own policies.
We size the right package and add-ons, plan the move from your existing agent with protection maintained throughout, and help you decide between Wayfinder MDR and a provider-run service. Licensing detail is on our SentinelOne licensing (opens in a new tab) pages, and pricing is always "ask us for a quote".
Contact us to discuss SentinelOne Singularity.
How we help with endpoint security
We are an independent UK IT and cyber security provider. We supply and support endpoint security from several vendors, so we can recommend what fits your devices, your people and your budget rather than one vendor's answer to everything.
- Start with what you have: we can review your current antivirus, EDR and Microsoft 365 licences before suggesting anything new
- Vendor-aware advice on EDR, XDR and managed detection and response, including CrowdStrike, SentinelOne, WatchGuard, Bitdefender, Sophos, Check Point, TrendAI and Cisco
- Deployment help: planning a rollout, replacing an existing product and setting sensible policies for device control, encryption and patching
- Policies and compliance: we help you map your controls to Cyber Essentials (opens in a new tab) and the NCSC's device guidance
- Ongoing support options, such as policy tuning, renewals and regular reviews, agreed and confirmed at quote
We work with businesses, schools, charities and public sector organisations. Tell us about your devices and we will suggest a sensible next step.
Frequently asked questions
What is SentinelOne Singularity?
SentinelOne Singularity is a security platform that protects endpoints, servers and cloud workloads from one agent and console. Its agent uses on-device AI to prevent, detect and respond to threats autonomously, with EDR and XDR from Singularity Complete and identity, AI-assisted investigation and managed services as options.
Is SentinelOne an EDR?
Yes. SentinelOne's EDR is part of Singularity Complete and the packages above it. It records device activity, links related events into Storylines and gives you investigation and response tools. The lower Core and Control packages focus on prevention and device control.
Can SentinelOne roll back ransomware?
Yes, on supported systems. The agent can reverse the changes a detected attack made, including encrypted files. It is a valuable recovery aid but does not replace independent, immutable backups.
What is Purple AI?
Purple AI is SentinelOne's AI security analyst within the Singularity platform. It lets analysts ask questions in natural language instead of writing queries, summarises activity and helps triage alerts. Ask us how it is licensed for your package.
Does SentinelOne work offline?
Yes. Detection and response run on the device, so protection continues without a connection. Events sync to the console when the device reconnects.
Does SentinelOne replace Microsoft Defender?
It replaces Defender as the primary antivirus and EDR on the devices it protects; on Windows, Microsoft Defender Antivirus steps back into passive or disabled mode when another antivirus product is primary. Microsoft 365 protections for email and identity carry on as before.
Still have a question about SentinelOne Singularity?
Ask us and a member of our team will get back to you.
More endpoint security guides
 Vigilance MDRSentinelOne's managed detection and response service, now Wayfinder MDR, explained.CrowdStrike vs SentinelOne vs DefenderA three-way EDR comparison: architecture, platforms, XDR depth, MDR and licensing.
 Falcon Insight XDRCrowdStrike's EDR, unified with identity, cloud and mobile telemetry, and how we supply Falcon.EDRWhat endpoint detection and response records, how it detects attacks and the response actions it gives you.XDRHow XDR correlates endpoint, identity, email, network and cloud signals, native vs open XDR, and XDR vs SIEM.Prevent ransomwareTen practical steps to stop ransomware reaching, running on and spreading from your laptops and servers, and to recover if it does.